
HN
@heloix_news
Fintech
How to Launch a Crypto Exchange Platform in Just 3 Days
#CryptoExchangePlatform#CryptocurrencyExchange#CryptoTrading
Comentar
1.1K
Mahesh P
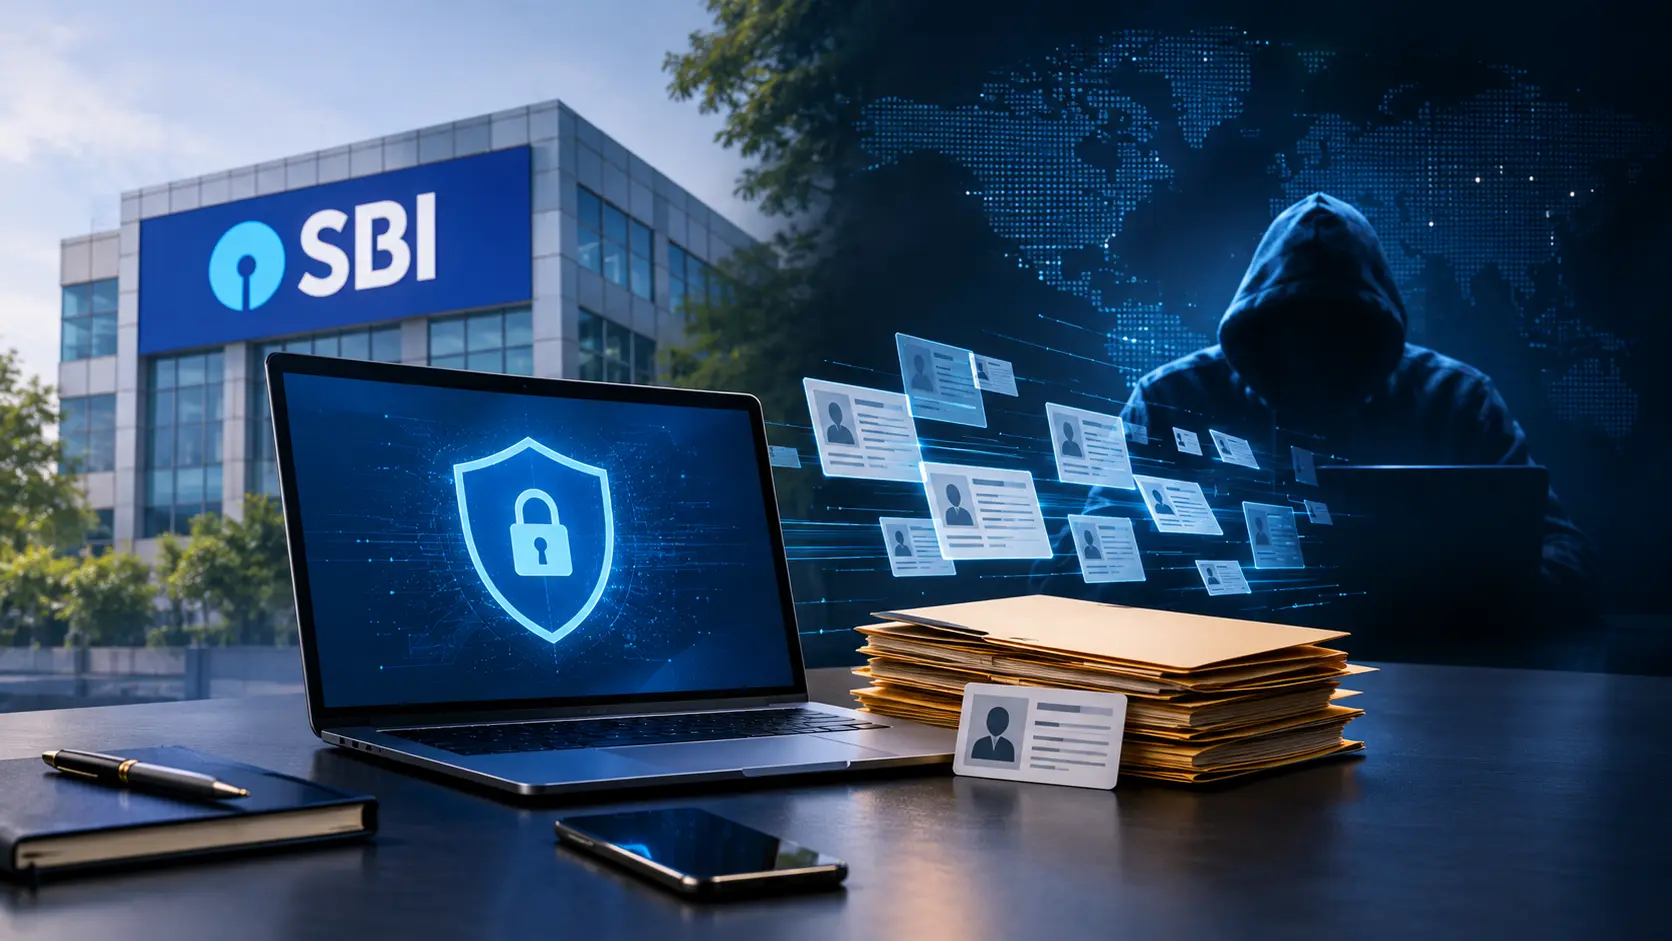
The State Bank of India (SBI) has launched a cybersecurity investigation after identifying 3,897 records containing personal information among data found circulating on the dark web. The country’s largest public sector bank disclosed the findings in a stock exchange filing on Wednesday, October 21, 2026.
The bank began examining the potential breach after receiving alerts from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In). During an initial assessment of approximately 3.75 lakh records reportedly available on the dark web, SBI identified 3,897 entries containing personally identifiable information.
The investigation follows a claim made last week by a threat actor operating under the name “Siriusim”. In a post on BreachForums, a website associated with the trading of stolen data, the individual claimed to have obtained around 3.75 lakh SBI customer records and 2,722 PDF documents allegedly connected to the bank.
The claim came to wider attention on October 16 after it was flagged by the X account CyberPulse56.
According to the listing, the dataset included a CSV file containing approximately 3.75 lakh rows, alongside the PDF documents. The person behind the post also shared four sample records to support the claim.
The Free Press Journal reviewed these samples and reported that the phone numbers appeared to be genuine. Much of the information seemed to relate to loan applications, while some records were associated with savings account applications and customer acquisition activities.
However, the full extent and authenticity of the alleged leak have yet to be established.
Following the alerts, SBI activated its cyber incident response procedures and brought in an independent cybersecurity agency empanelled with CERT-In.
The agency has been tasked with verifying whether the exposed records are authentic, determining how the information may have been accessed and identifying the potential security implications. SBI has also said it is taking preventive and corrective steps as part of its response.
Several key details remain unclear. Investigators have yet to establish how the information was obtained or when the records were created. It is also uncertain whether the data relates to a recent incident or an older exposure.
SBI has not disclosed how many of the 3,897 records identified during its preliminary review belong to existing customers.
The information reportedly included in the sample records has raised concerns about the possible consequences for affected individuals. The samples contained identity verification documents, suggesting that the potential exposure could involve more sensitive information than names and telephone numbers alone.
Such documents can present longer-term risks if misused for identity fraud or other unauthorised activities. Unlike a compromised password, identity documents may be difficult to replace, potentially making the consequences of an exposure more persistent.
The findings are preliminary, however, and the bank's investigation will need to establish which records are genuine and whether the information has been used improperly.
The incident also draws attention to the obligations of organisations that handle personal information under India's data protection framework.
The Digital Personal Data Protection Act requires organisations to implement reasonable security safeguards to protect personal data and meet applicable breach-notification requirements. Certain violations can attract financial penalties of up to Rs 250 crore.
As the investigation progresses, the findings could help clarify the nature of the suspected exposure and whether any security failures contributed to it.
This is not the first time SBI has faced scrutiny over the security of customer information. In 2019, the bank disputed a TechCrunch report concerning an unprotected server, stating that its own investigation had found no evidence of a data breach.
The current case remains under investigation, and the bank has not yet confirmed the full scope or origin of the data found on the dark web.
Further details are expected as cybersecurity experts continue to examine the records and assess the potential impact on customers.
Por favor, para publicar um comentário
Nenhum comentário ainda
Seja o primeiro a compartilhar sua opinião.
@heloix_news
Fintech
@heloix_news
Fintech
@heloix_news
Fintech
Inscreva-se para receber as últimas novidades sobre tecnologia, crescimento de negócios e transformação digital.